Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×
Traditional or static Multi-Factor Authentication (MFA) verifies every user the same way, no matter the context, which leaves dangerous security gaps.
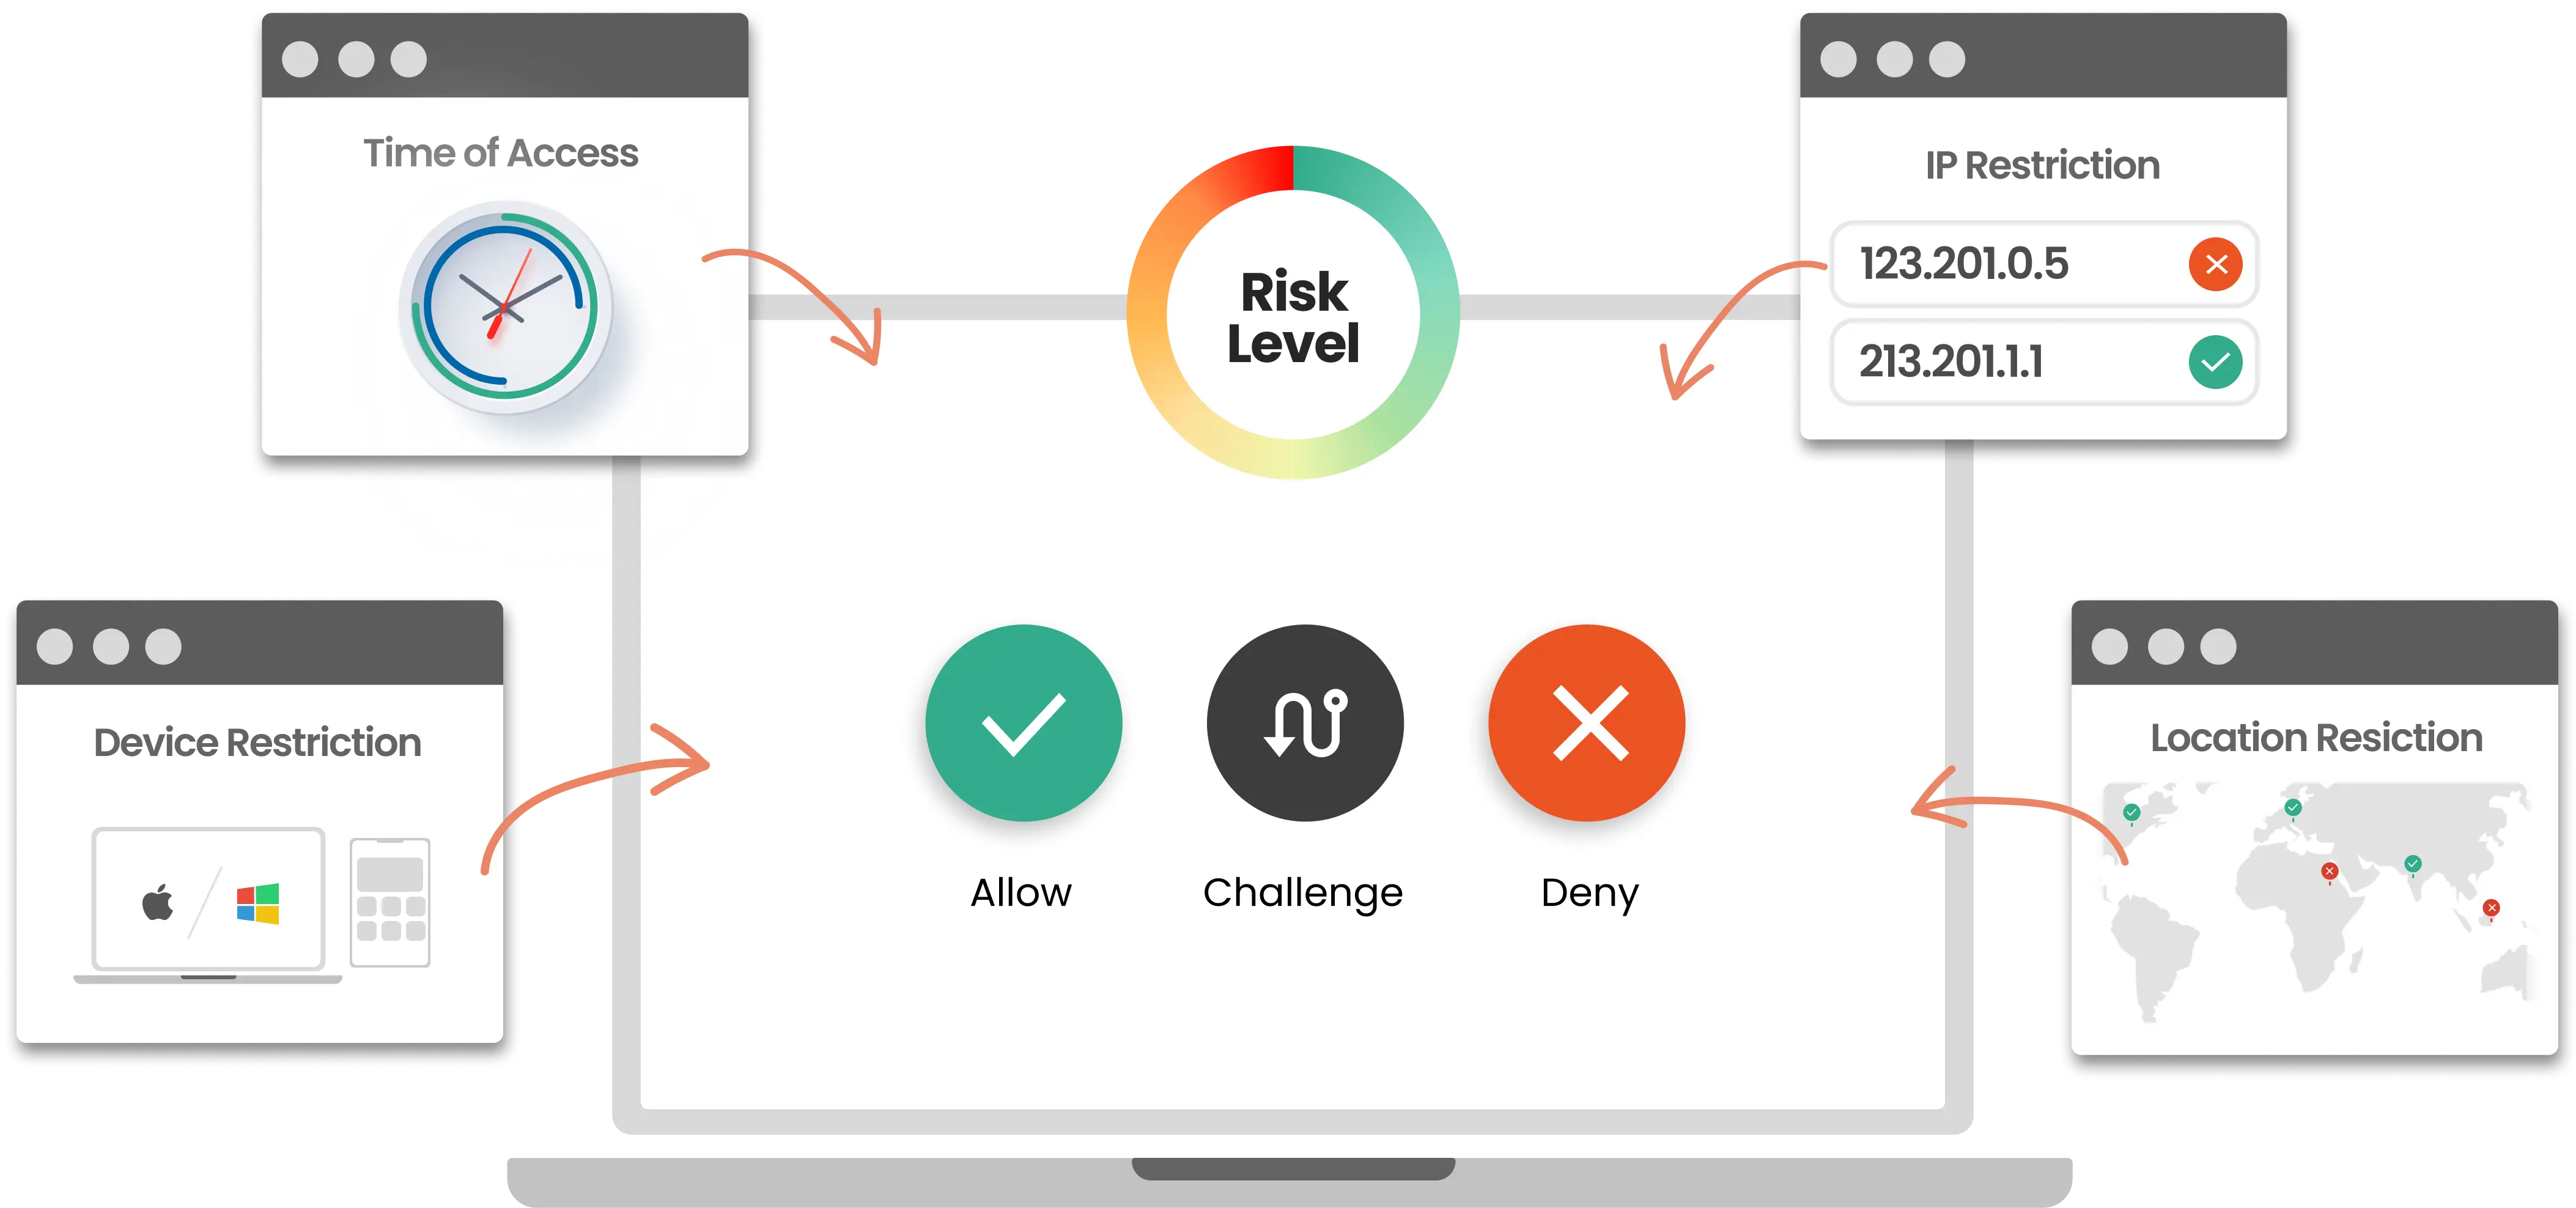
However, with miniOrange Adaptive/Risk-Based MFA, every login is evaluated in context: IP, device, location, time, and behavior, so high‑risk login attempts are stepped up, challenged, or blocked, and low‑risk access is kept smooth. This adaptive approach prevents unauthorized access, improves user experience, and helps you meet modern compliance requirements.
miniOrange risk-based authentication software delivers adaptive protection that fits seamlessly into your existing IAM stack across cloud, on‑prem, and multi-tenant cloud environments.

Strengthen authentication with risk-aware MFA that applies additional verification only when suspicious activity or elevated risk is detected.

Define adaptive policies using contextual signals and custom rules to enforce authentication requirements based on risk and access scenarios

Continuously evaluate authentication requests and dynamically restrict, challenge, or deny access when suspicious conditions are identified.

Analyze user behavior, device posture, location, and network context to calculate risk levels and make intelligent authentication decisions.

Combine multiple risk signals using AND/OR operators to precisely define when to trigger, step up, or block authentication attempts.

Continuously reassess session behavior after login and dynamically enforce stronger authentication or terminate access when risk levels change.
The RBA risk score is generated in real time and categorizes each login attempt into low, medium, or high risk based on contextual signals.
If risk-based authentication detects a target that may pose a significant risk, the system may ask for more MFA techniques or refuse access completely. For example, When a consumer of Internet banking asks for a significant transfer of funds to an external account, a high-risk RBA score is generated. Such a sensitive transaction would prompt additional MFA methods, even if typical risk indications such as the IP address and user behavior check out.
In medium risk-based authentication, the user signs into the account from a device they are unfamiliar with, even though their credentials are correct, the connection could be deemed as medium risk. The system gives the user access as soon as they enter the correct extra information. Entry will be refused if they don't work.
The user is given access to the account and is not prompted for additional authentication factors if risk-based authentication software finds that the connection is low-risk. Low risk users typically log into their accounts from the same device or location. Another low-risk connection is a virtual private network (VPN). When a remote worker accesses a digital asset from a known geolocation, such as their home office and from a known IP address, a low risk score is produced.
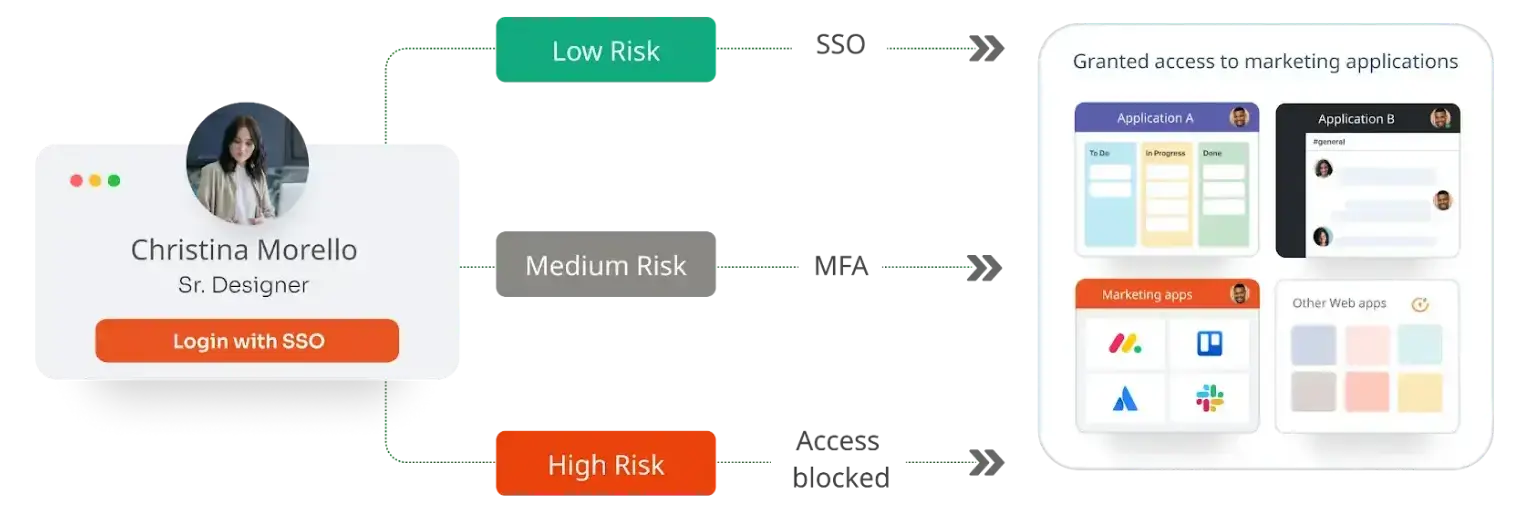
Use risk‑based authentication to secure any customer‑facing app, website, or portal where login attempts can be evaluated for risk.
Explore miniOrange app Integration Catalog





Keep login verifications frictionless and amplify security posture with the miniOrange Risk-Based Authentication software.
Risk-based/adaptive authentication solution reduces fraud, account takeover, and credential attacks through real-time risk scoring, context-aware access policies, and adaptive MFA that steps up only when risk is high.

miniOrange helps you align with security and privacy regulations such as HIPAA, GDPR, DPDP, PCI DSS, and more.

From a centralized dashboard, admins manage user activities, risk-based policies, and access controls across all apps.
*Please contact us to get volume discounts for higher user tiers.