Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×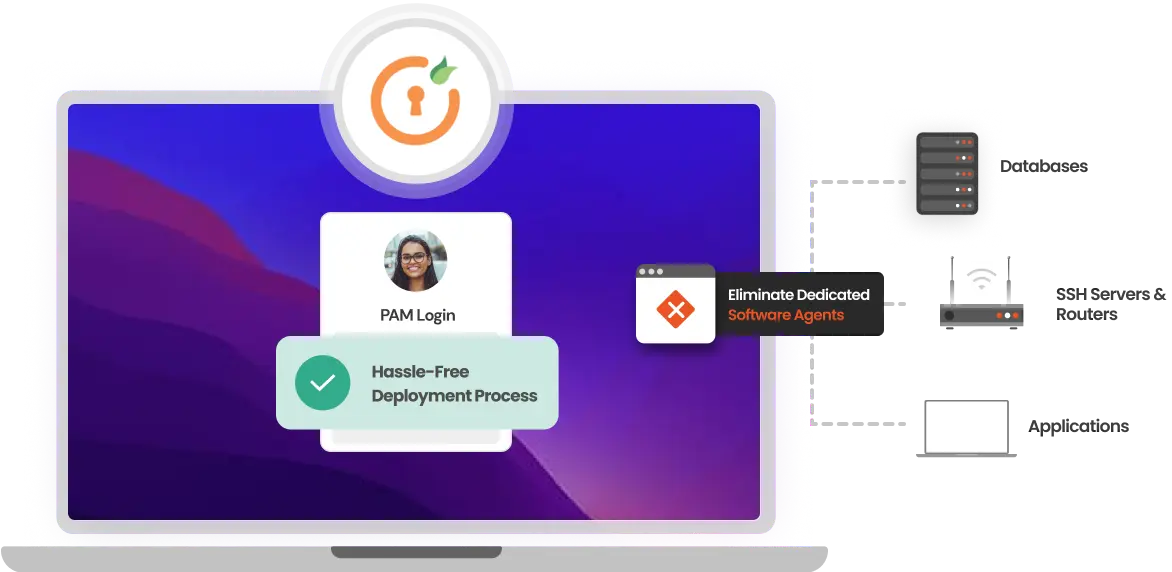
Agentless Privileged Access Management (PAM) secures and monitors privileged sessions without ever placing software on the target endpoint. Instead of deploying agents to every server, database, or network device, PAM brokers each connection. Thus, ensuring authentication, authorization, and session recording in real time.
This approach removes the biggest friction in traditional PAM: endpoint sprawl. Security teams get the same visibility and control, such as password vaulting, just-in-time access, and session monitoring. They get all of it without the operational drag of installing, updating, and troubleshooting agents across thousands of machines.
Explore comprehensive PAM features, integration methods, compliance benefits, and everything you need in one place.
Your download should start now. If not, please email us at idpsupport@xecurify.com.
Please enter a valid email-id
Agentless architecture fastens the onboarding process and reduces maintenance work across every endpoint.

No agents, plugins, or client software are required on target servers, databases, or network devices. Access is brokered through PAM, keeping endpoints untouched.

With no endpoint agents to package, install, upgrade, or troubleshoot, teams onboard new infrastructure faster. What used to take a change-management cycle now takes an afternoon.

Administrators reach Windows, Linux, databases, and network devices directly from a browser. No VPN client, no RDP software, and no SSH client are required to get started.

No agent upgrades, no compatibility testing, and no endpoint maintenance to track. One centralized console manages every connection, credential, and session.

Access AWS, Azure, GCP, Linux, Windows, databases, and network devices using their existing native protocols. One platform covers on-prem, cloud, and multi-cloud environments alike.

Fewer components to deploy means less maintenance and reduced operational complexity. Teams onboard new systems faster and spend less time fighting agent issues.
miniOrange packs enterprise-grade privileged access controls into a single agentless platform, so security teams protect every credential and session without adding infrastructure.
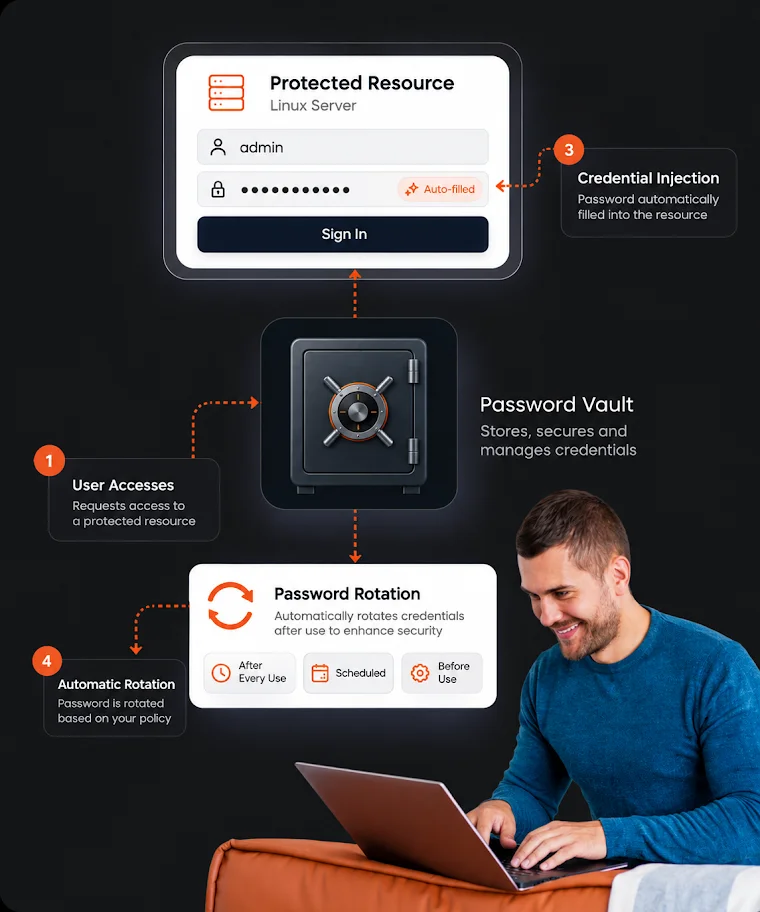
Store, encrypt, and automatically rotate privileged credentials with privileged password management so no password sits static, and no shared secret becomes a standing risk.
Know More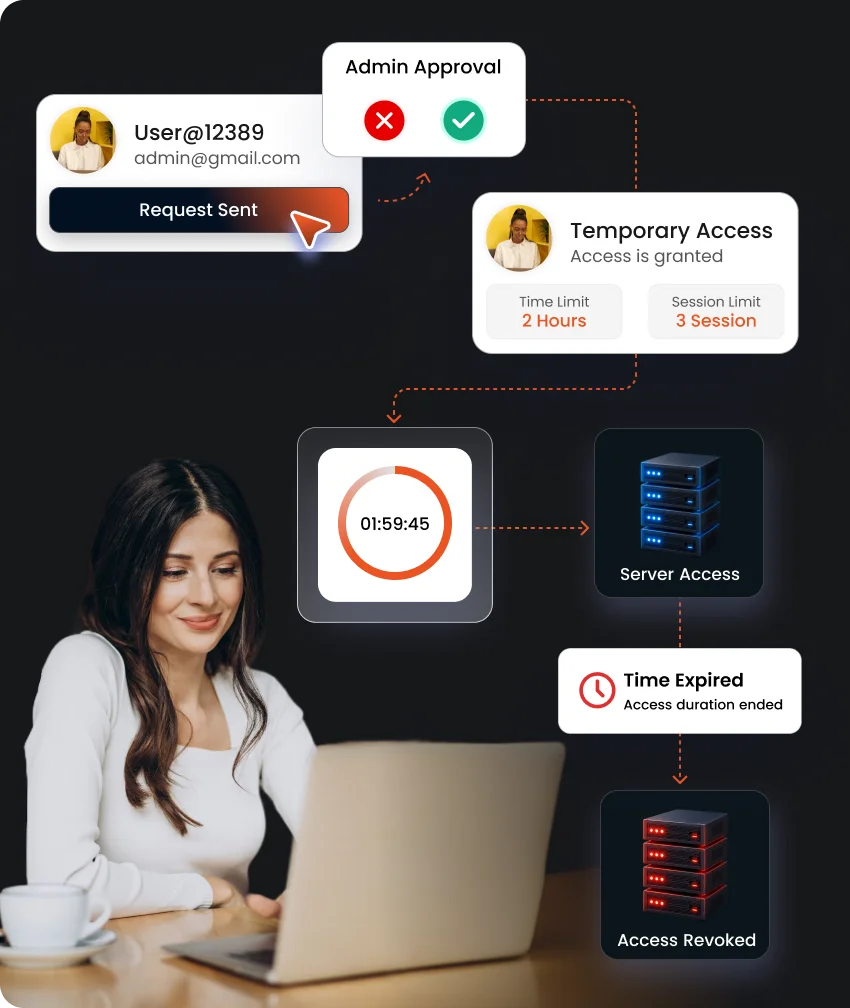
Grant just-in-time privileged access only when it's needed and revoke it the moment the task is done, eliminating standing privileges that attackers exploit.
Know More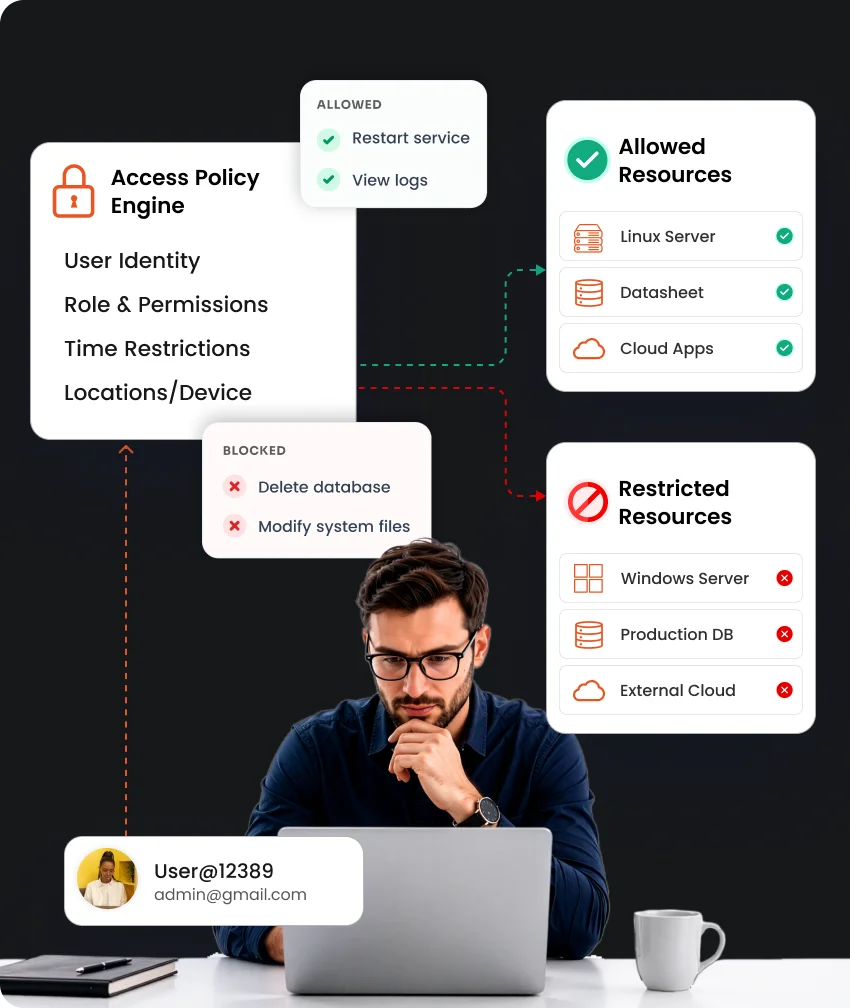
Define precisely who can access which systems, at what times, and under what conditions, down to the individual command or resource.
Know More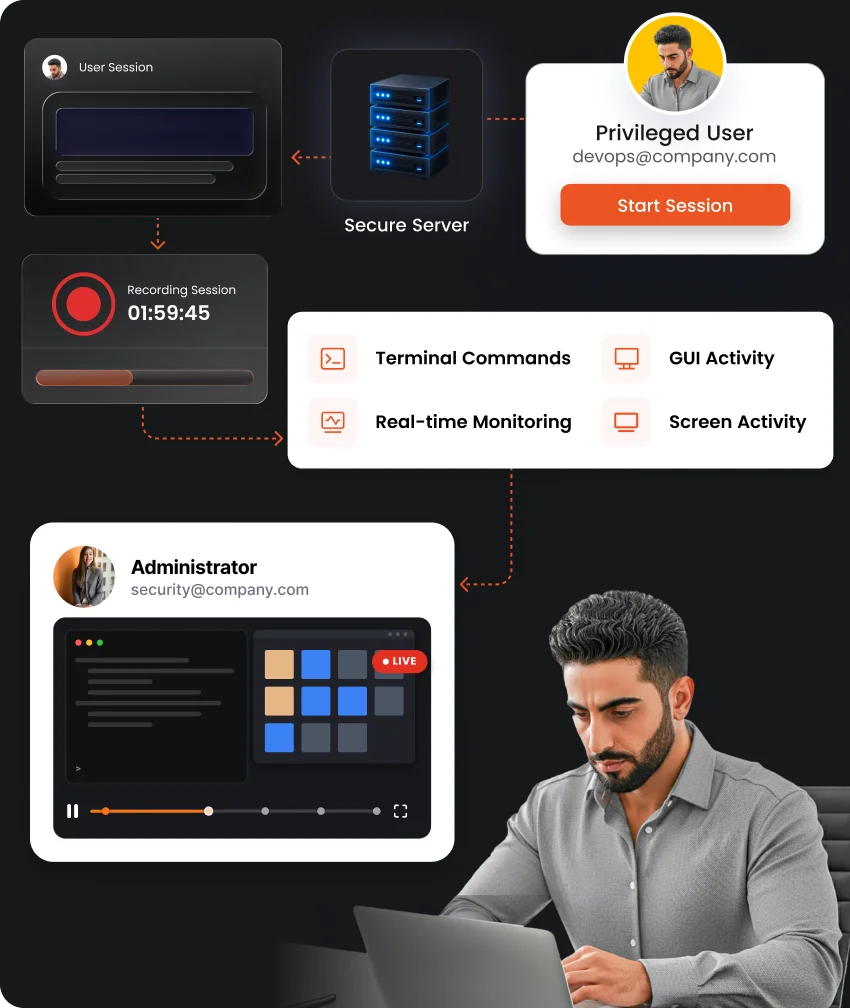
Record and monitor every privileged session in real time, giving security teams full visibility and an audit trail for every action taken.
Know More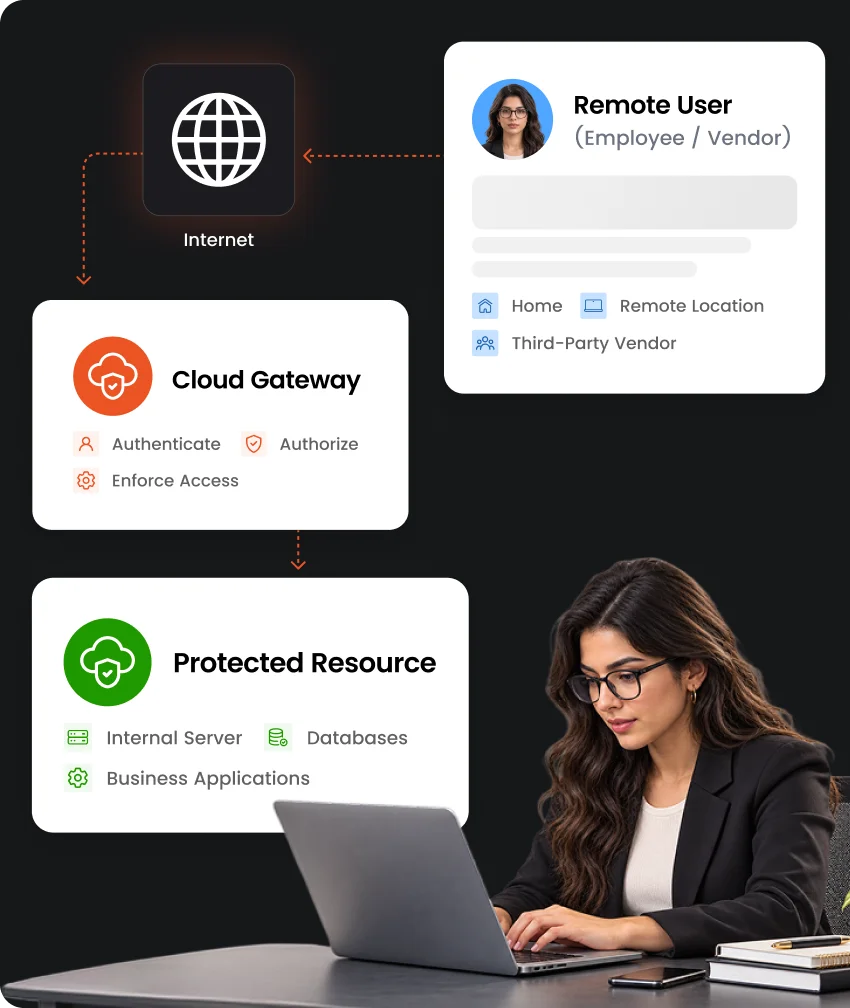
Secure remote connections to critical systems without exposing them through VPNs or open ports, closing off a common entry point for attackers.
Know More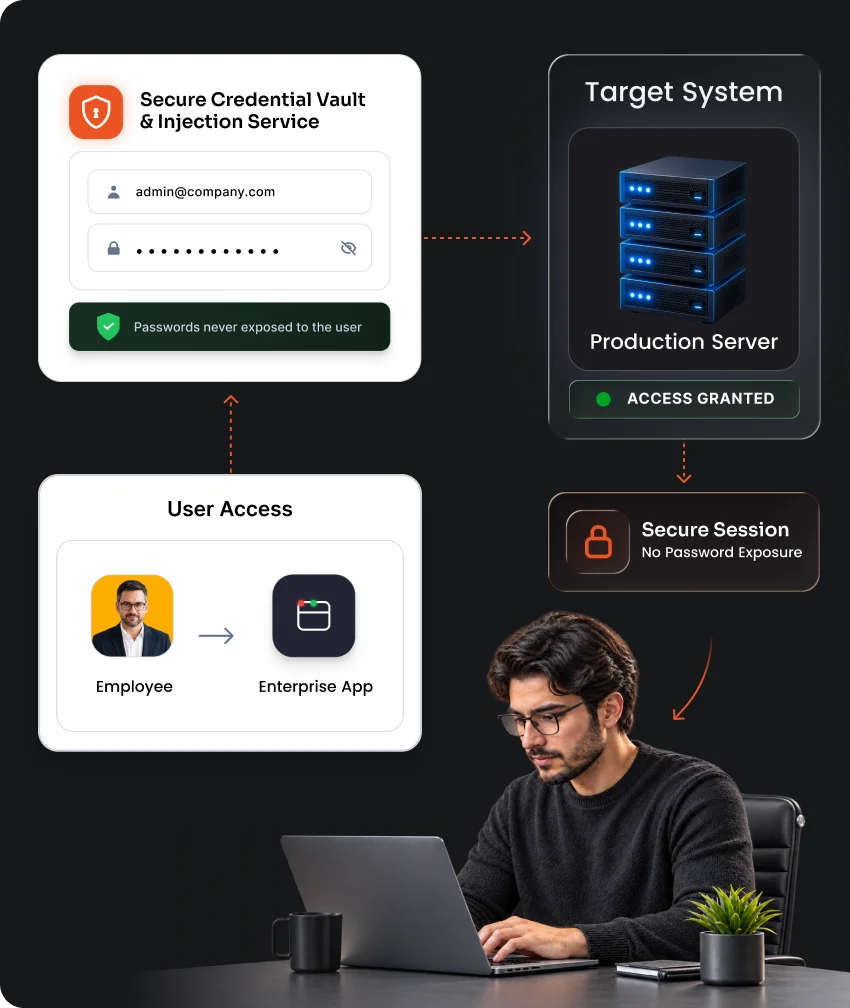
Automatically inject privileged credentials into target systems and applications, allowing users to access resources without viewing or handling sensitive passwords.
Know More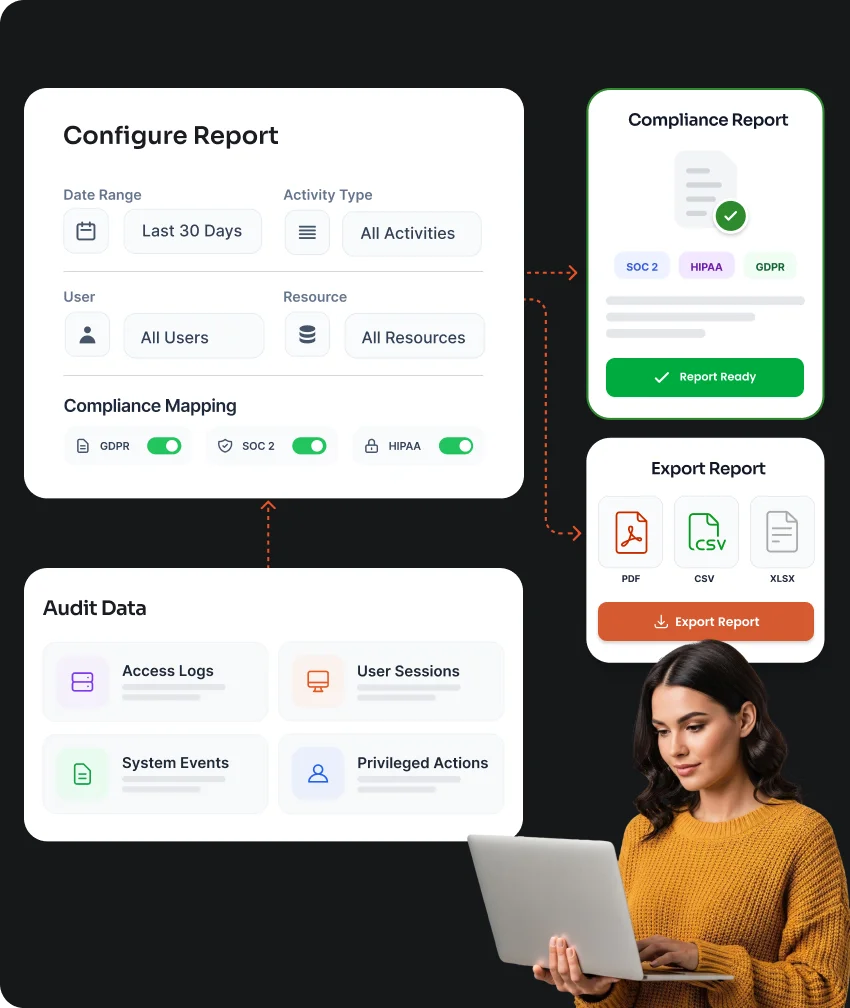
Generate detailed, configurable audit reports that map directly to compliance frameworks like SOC 2, HIPAA, and GDPR, so auditors get what they need without extra manual work.
Know MoreEvery privileged session is anchored to a verified identity, not just a static credential, closing the gaps that credential-only tools leave open.
Deploy across cloud, on-premises, and hybrid environments without deploying or maintaining agents on every target system.
A dedicated support team is available around the clock to help with onboarding, troubleshooting, and audits, wherever your team operates.
Get enterprise-depth privileged access controls at affordable pricing, without compromising on capability.