

Shibboleth is a web-based software tool that supports single sign-on (SSO) between two applications or between two organizations. It is an open-source tool and is mainly used for Single Sign-On (SSO) using the SAML protocol. It can not implement SSO with protocols such as OAuth or OpenID Connect.
It helps sites make informed authorization decisions for accessing protected resources and provides federated identity-based authentication and authorization that allows cross-domain Single Sign-On (SSO) and removes the need for access credentials.
Components That Fall Under Shibboleth
Shibboleth web-based Single Sign-On (SSO) system contains three Components:
- Identity Provider (IDP) – An identity provider (IDP) creates, maintains, and manages user identities and information. Identity Providers are responsible for user authentication and providing required user information to the Service Provider (SP).
- Service Provider (SP) – The Service Provider (SP) receives authentication assertions from the Identity Provider and authenticates the user.
- Discovery Service (DS) – It helps the Service Provider to discover the user’s Identity Provider. It may be located anywhere on the web and most of the time does not require it.
Shibboleth SSO Workflow
The diagram below shows the common workflow of single sign-on (SSO) and interaction between the User, Identity Provider (IDP), and Service Provider (SP).
Shibboleth SSO flow with miniOrange IDP
The authentication process using an Identity Provider (IDP), takes place in the following steps:
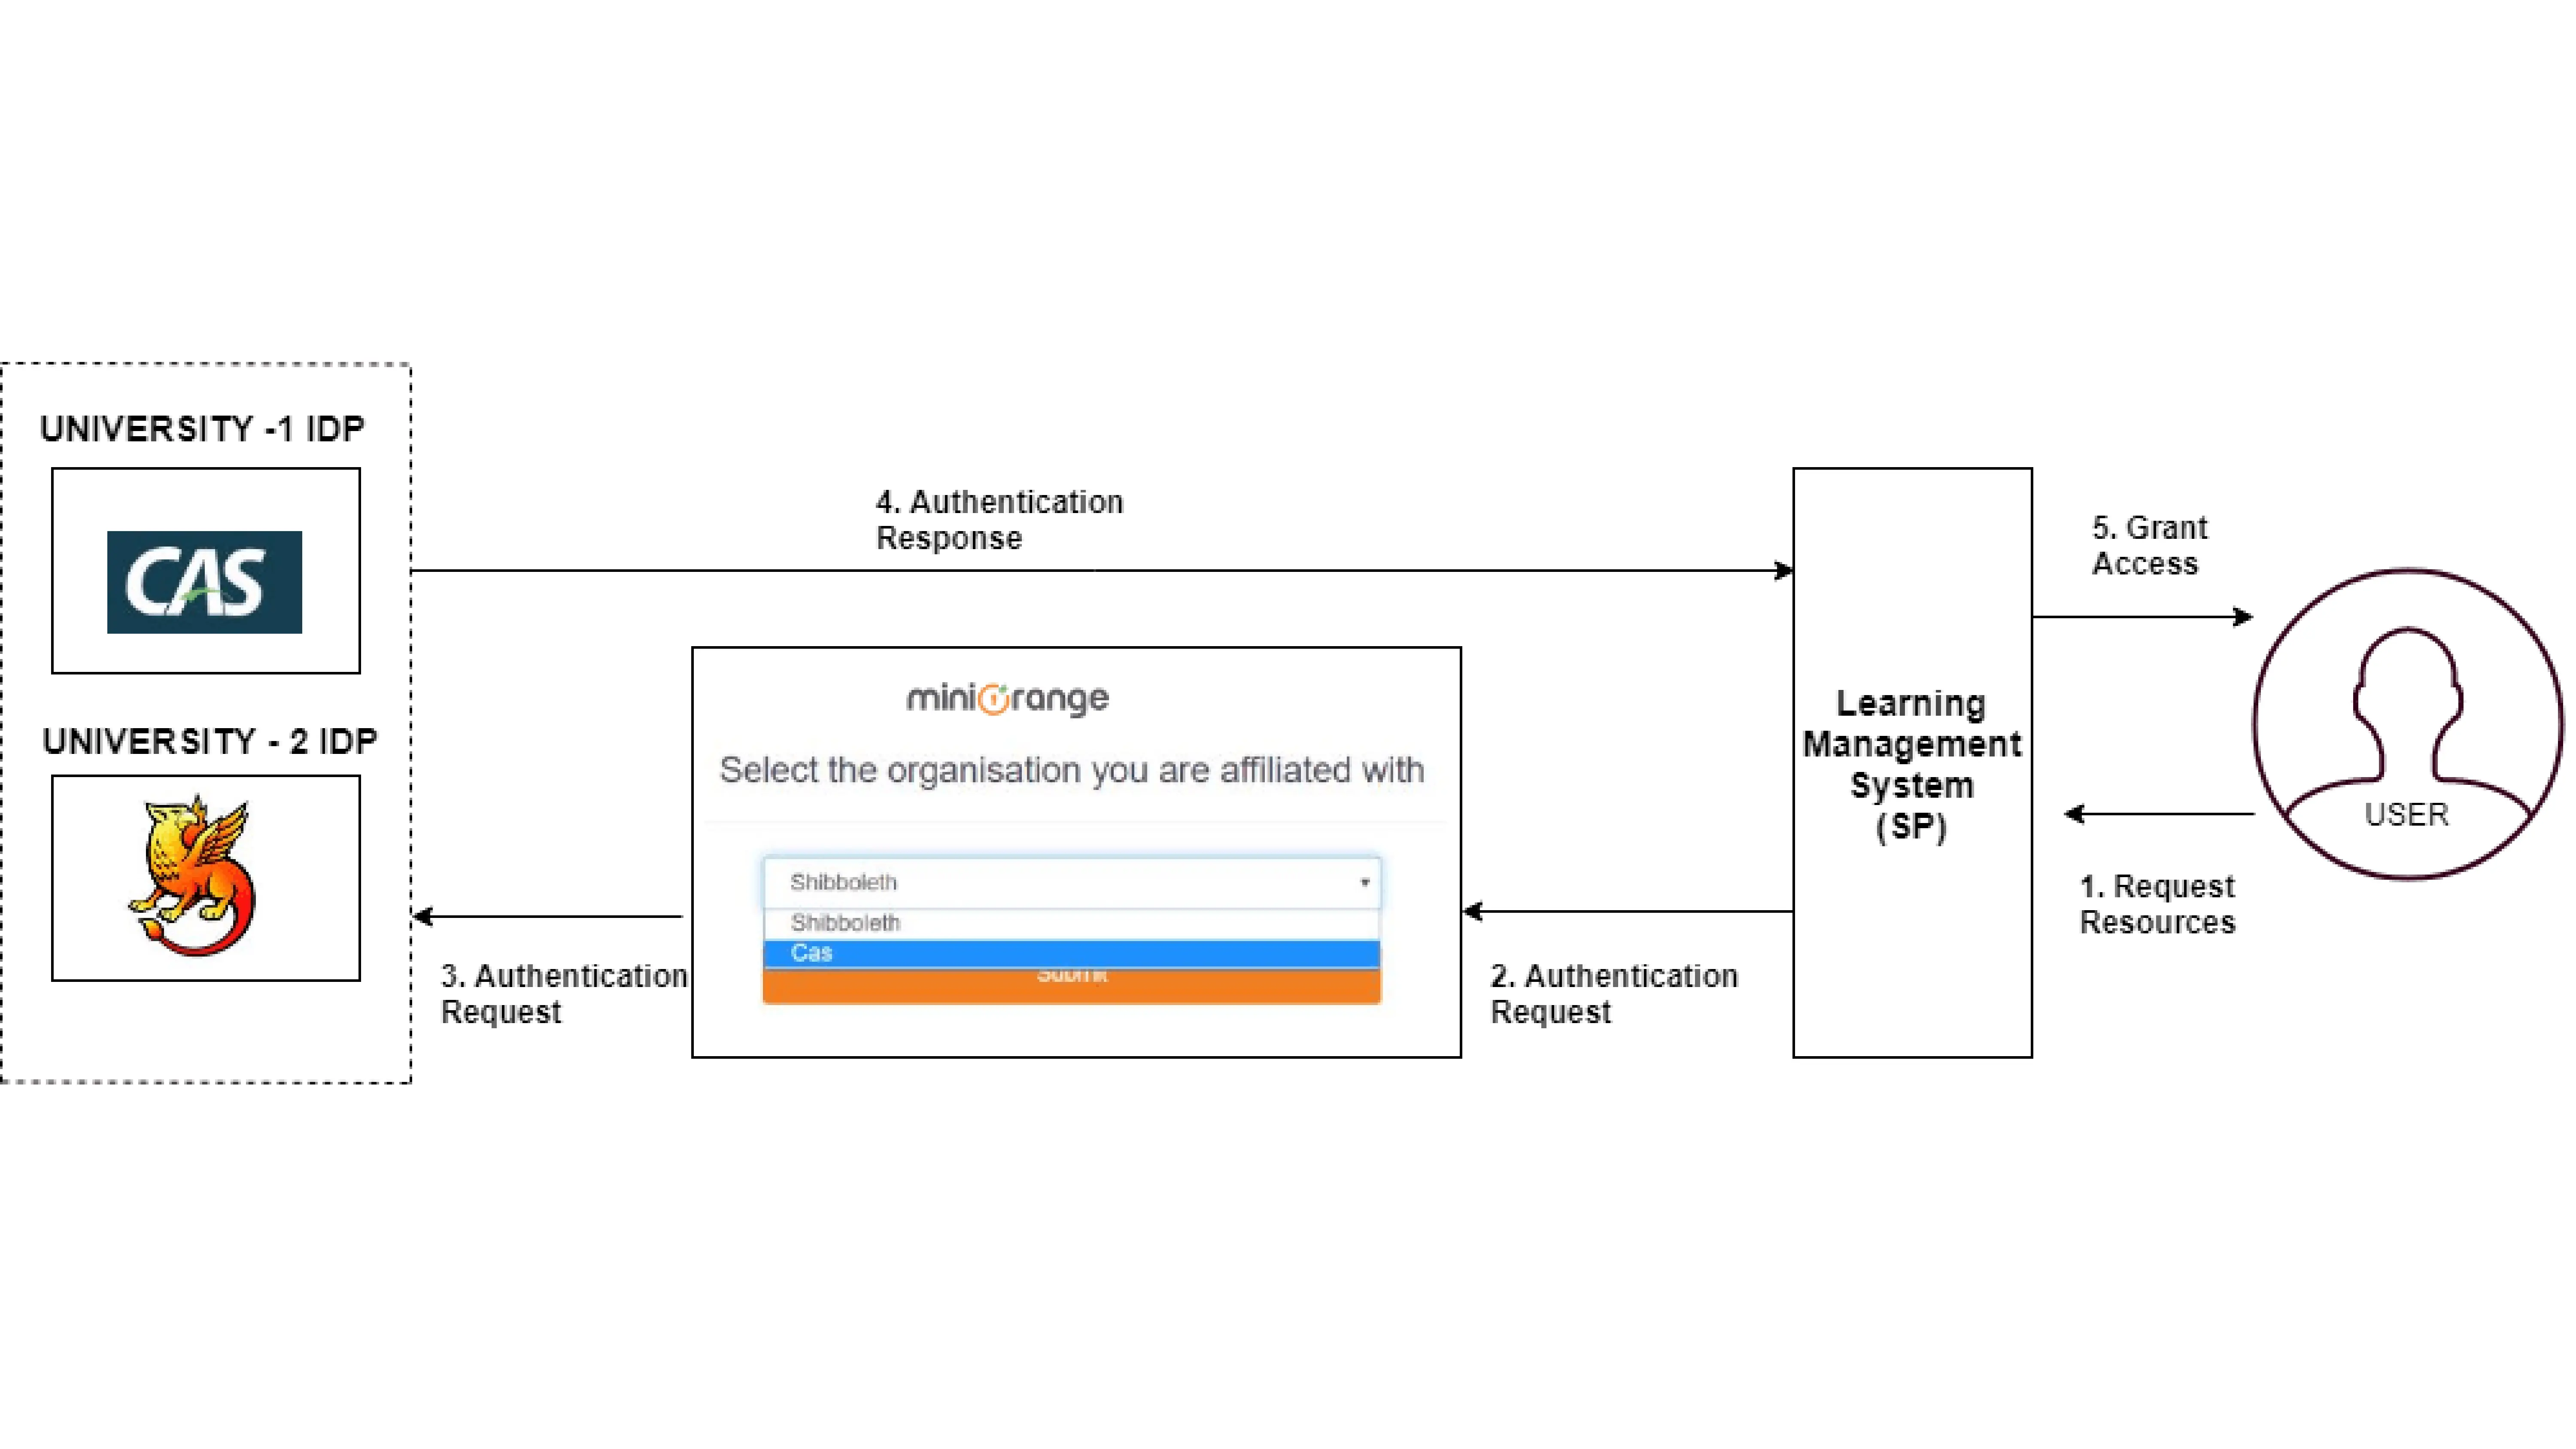
1. The user reaches for a Service provider (website) to access the resources.
2. Service Provider figures out the Identity Provider (IDP) with the help of the miniOrange discovery service and authenticates the user with the Identity Provider (IDP).
3. Identity Provider checks if any active session is going on if it is not, then it asks the user to enter the credentials, and the authentication request is sent to the IDP.
4. Identity Provider (IDP) sends an authentication response to the Service Provider (SP).
5. After authenticating the user with the Identity Provider (IDP), the Service Provider (SP) grants access to the user.
Authenticate IDPs without any external software
With the miniOrange SAML plugin, you can configure multiple IDPs registered with HAKA Federation. This allows users to authenticate with these IDPs without any external software installation like Shibboleth SP or a Gluu server. Get all your user details and choose to auto-provision users if necessary all from a single installation of a plugin.
Advantages of using miniOrange SSO with HAKA Federation
1. Easy to integrate. If your site has users from different universities and you want them to authenticate with their university account using HAKA then you can do that using this plugin. For example – if you have a site that has users from different universities, you can enable your users to sign in using their university account.
2. Easy to install. You only have to install and configure the Plugin once. This is useful if you are using hosting providers like WP Engine, which do not allow the installation of any external software to the server.
3. Easy to manage. If you install the Gluu server or Shibboleth a lot of customization will be needed just to make it work and then yearly maintenance of the servers add up as well. In contrast, the plugin is easy to set up and easily maintainable.
4. Cost-effective. Installation of the Gluu server or Shibboleth server is a costly affair. Yearly maintenance of the servers also adds up to the cost. In contrast, the plugin costs just a fraction of that.
5. Easy to use. Users have the ability to choose their university during login and authenticate using their university credentials.
Limitations of Shibboleth
1. Support limited protocols such as SAML.
2. Support and customization are not available because it is open-source, unlike other vendors who provide full support.
3. It is more complex to set up and configure. The configuration is more involved.
4. It only supports SAML 1 and SAML 2 and features up to Shibboleth 2.4 protocols.
5. The Shibboleth IdP V3 software has reached its End of Life and is no longer supported.
Shibboleth vs. miniOrange IDP
| Feature | Shibboleth | miniOrange IDP |
|---|---|---|
| Multi-Protocol support | Supports only a few authentication protocols, like SAML1 and SAML 2 | Fully supports all protocols for Authentication. miniOrange supports SAML, SAML 2, JWT, OAuth, OpenID Connect, CAS and more. |
| Configuration and Setup | Require a more complex setup and configuration. | Easy to set up and configure |
| Support | As it is open-source limited support is provided. | miniOrange provides 24*7 active support. |
| Multiple SP and IDP support | It requires customization. | miniOrange can act as an Identity broker and support authentication for multiple apps and IDPs |
Conclusion
The web-based open-source tool supports single sign-on (SSO) between two applications or organizations using SAML protocol and cannot be implemented using other protocols such as OAuth or OpenID connect.
The common workflow of Shibboleth single sign-on (SSO) is the interaction between User, Identity Provider (IDP), and Service Provider (SP) where SP figure outs the IDP with the help of miniOrange discovery service.
Leave a Comment